March 2003
Intermediate to advanced
308 pages
9h 36m
English
Why is authentication needed in an LDAP directory? Remember that LDAP is a connection-oriented, message-based protocol. The authentication process is used to establish the client’s privileges for each session. All searches, queries, etc. are controlled by the authorization level of the authenticated user.
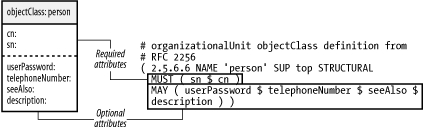
Figure 2-8 describes the person
object class and gives you an idea of what other attributes are
available for the cn=gerald
carter entry in Figure 2-1. In
particular, you will need to define a userPassword
attribute value to further explore LDAP authentication.
 |
The LDIF representation for the expanded version
cn=gerald
carter is:
dn: cn=gerald carter,ou=people,dc=plainjoe,dc=org
objectClass: person
cn: gerald carter
sn: carter
telephoneNumber: 555-1234
userPassword: {MD5}Xr4ilOzQ4PCOq3aQ0qbuaQ=  =
We have added an attribute named userPassword.
This attribute stores a representation of the credentials necessary
to authenticate a user. The prefix (in this case,
{MD5}) describes how the credentials are encoded.
The value in this case is simply the Base64 encoding of the MD5 hash
of the word “secret.”
RFC 2307 defines prefixes for several encryption algorithms. These
are vendor-dependent, and you should consult your
server’s documentation to determine which are
supported. Generating userPassword values will be covered in more detail in the context ...
Read now
Unlock full access


 O’Reilly covers everything we've got, with content to help us build a world-class technology community, upgrade the capabilities and competencies of our teams, and improve overall team performance as well as their engagement.I wanted to learn C and C++, but it didn't click for me until I picked up an O'Reilly book. When I went on the O’Reilly platform, I was astonished to find all the books there, plus live events and sandboxes so you could play around with the technology.I’ve been on the O’Reilly platform for more than eight years. I use a couple of learning platforms, but I'm on O'Reilly more than anybody else. When you're there, you start learning. I'm never disappointed.I'm always learning. So when I got on to O'Reilly, I was like a kid in a candy store. There are playlists. There are answers. There's on-demand training. It's worth its weight in gold, in terms of what it allows me to do.