December 2018
Intermediate to advanced
226 pages
4h 57m
English
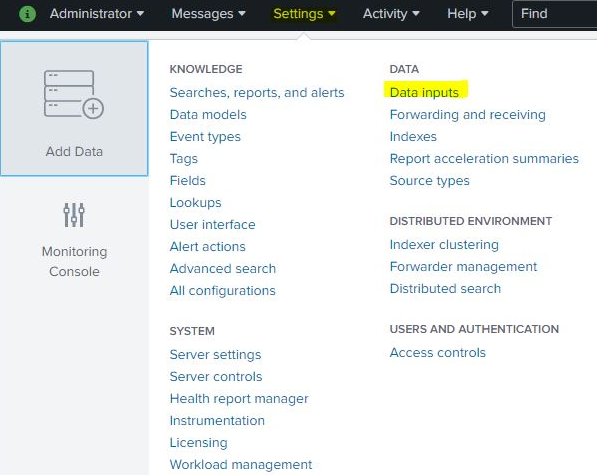
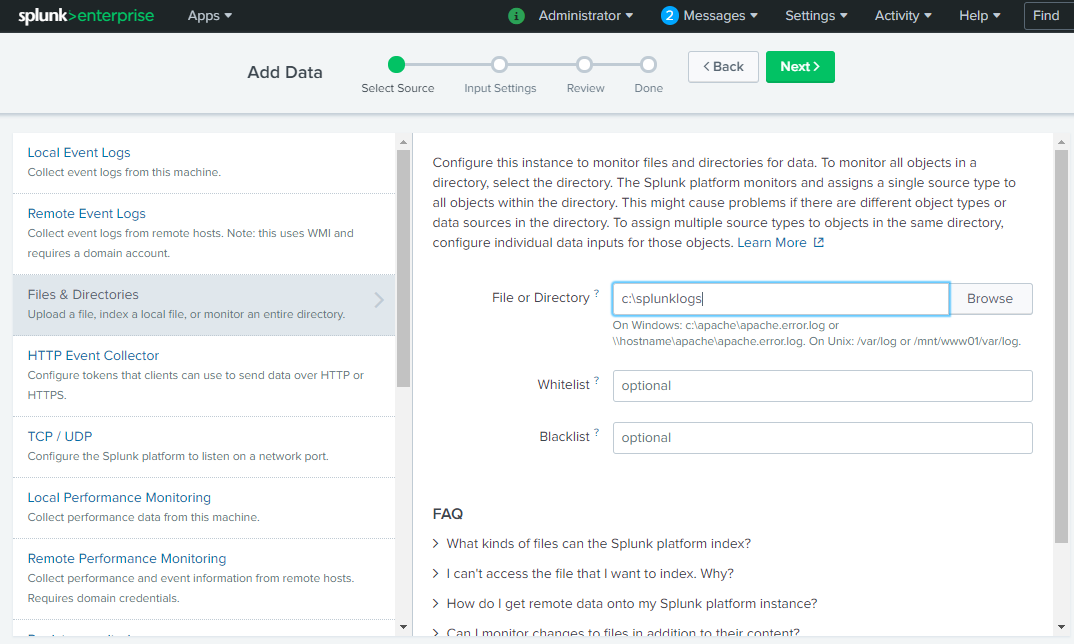
In this step, we configure Splunk to monitor a specific folder in the local machine for any new data. Data would typically be in a comma-separated format generated from a Python script written in this particular folder. Listed are the steps to configure Splunk for monitoring the folder:
Select Data inputs from the Settings drop-down menu:
Read now
Unlock full access


 O’Reilly covers everything we've got, with content to help us build a world-class technology community, upgrade the capabilities and competencies of our teams, and improve overall team performance as well as their engagement.I wanted to learn C and C++, but it didn't click for me until I picked up an O'Reilly book. When I went on the O’Reilly platform, I was astonished to find all the books there, plus live events and sandboxes so you could play around with the technology.I’ve been on the O’Reilly platform for more than eight years. I use a couple of learning platforms, but I'm on O'Reilly more than anybody else. When you're there, you start learning. I'm never disappointed.I'm always learning. So when I got on to O'Reilly, I was like a kid in a candy store. There are playlists. There are answers. There's on-demand training. It's worth its weight in gold, in terms of what it allows me to do.