January 2020
Intermediate to advanced
428 pages
10h 34m
English
When a user logs in to the system, a token is generated based on the payload (that is, the user information and secret key). The generated token is stored locally. For all future requests, this token is added to the request and the application will validate the token before responding to the request:
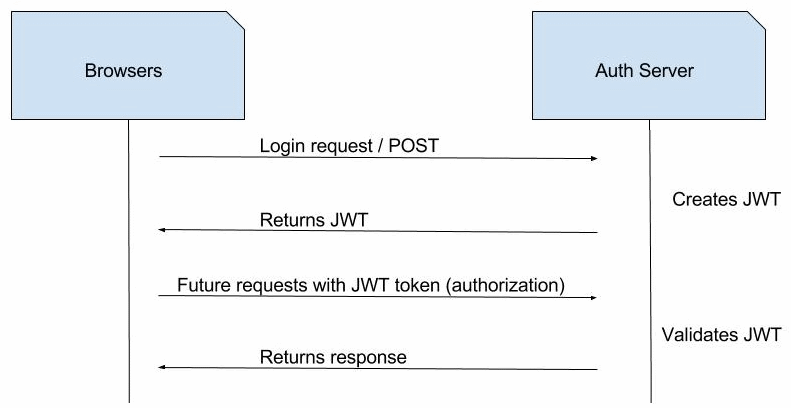
The token will be in this format:
Authorization: Bearer <token>
In JHipster, we use JJWT (short for Java-based JSON Web Tokens) from Okta. This is a simplified builder pattern-based library used to generate and sign the token as a producer and parse and validate the token as a consumer.
Read now
Unlock full access


 O’Reilly covers everything we've got, with content to help us build a world-class technology community, upgrade the capabilities and competencies of our teams, and improve overall team performance as well as their engagement.I wanted to learn C and C++, but it didn't click for me until I picked up an O'Reilly book. When I went on the O’Reilly platform, I was astonished to find all the books there, plus live events and sandboxes so you could play around with the technology.I’ve been on the O’Reilly platform for more than eight years. I use a couple of learning platforms, but I'm on O'Reilly more than anybody else. When you're there, you start learning. I'm never disappointed.I'm always learning. So when I got on to O'Reilly, I was like a kid in a candy store. There are playlists. There are answers. There's on-demand training. It's worth its weight in gold, in terms of what it allows me to do.