March 2018
Beginner to intermediate
576 pages
13h 29m
English
The field picker gives us easy access to the fields (currently defined) for the results of our query. Splunk will extract some fields from event data without your help such as: host, source, and sourcetype values, timestamps, and others. Additional fields to be extracted can be defined by you. Clicking on any field presents us with the details about that field in our current search results:
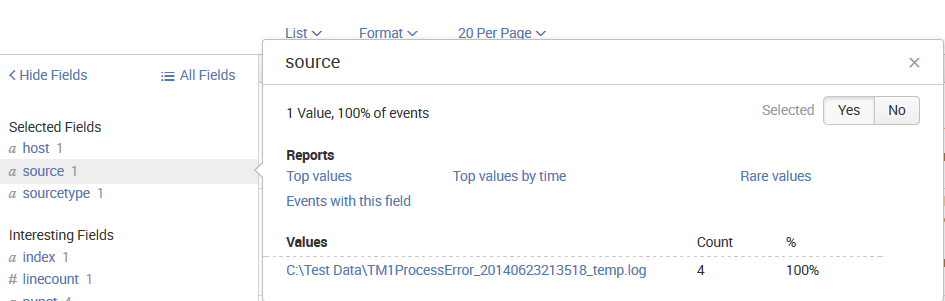
As we go through the following items in this widget, we see a wealth of information right away:
Read now
Unlock full access


 O’Reilly covers everything we've got, with content to help us build a world-class technology community, upgrade the capabilities and competencies of our teams, and improve overall team performance as well as their engagement.I wanted to learn C and C++, but it didn't click for me until I picked up an O'Reilly book. When I went on the O’Reilly platform, I was astonished to find all the books there, plus live events and sandboxes so you could play around with the technology.I’ve been on the O’Reilly platform for more than eight years. I use a couple of learning platforms, but I'm on O'Reilly more than anybody else. When you're there, you start learning. I'm never disappointed.I'm always learning. So when I got on to O'Reilly, I was like a kid in a candy store. There are playlists. There are answers. There's on-demand training. It's worth its weight in gold, in terms of what it allows me to do.