July 2026
Intermediate
480 pages
20h 9m
English
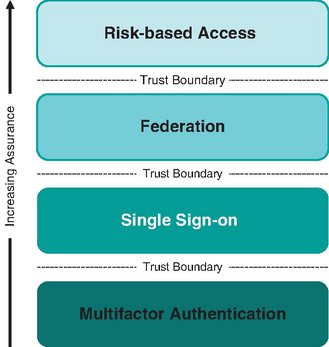
Identity and access management (IAM) sits at the center of cybersecurity assurance. It defines how trust is established, maintained, and revoked across every layer of an organization’s technology ecosystem. From onboarding new users to managing privileged credentials and machine identities, the effectiveness of these controls determines whether the enterprise can enforce least privilege and maintain accountability in a complex digital environment. As threat actors increasingly exploit identity weaknesses rather than technical vulnerabilities, understanding and auditing this domain has become one of the most critical elements of enterprise security governance.
Modern identity systems extend far beyond usernames and passwords. They integrate with cloud directories, federated partners, and automated workflows that grant and revoke access across thousands of systems in real time. This chapter examines the full life cycle of identity assurance—from how user and service identities are created and governed to how authentication, elevation, and emergency access are controlled and monitored. It also addresses how evidence from disparate systems such as HR platforms, identity providers, and privileged access management (PAM) tools must align to demonstrate compliance and operational integrity.
For organizations building AI-driven or cloud-native architectures, ...
Read now
Unlock full access


 O’Reilly covers everything we've got, with content to help us build a world-class technology community, upgrade the capabilities and competencies of our teams, and improve overall team performance as well as their engagement.I wanted to learn C and C++, but it didn't click for me until I picked up an O'Reilly book. When I went on the O’Reilly platform, I was astonished to find all the books there, plus live events and sandboxes so you could play around with the technology.I’ve been on the O’Reilly platform for more than eight years. I use a couple of learning platforms, but I'm on O'Reilly more than anybody else. When you're there, you start learning. I'm never disappointed.I'm always learning. So when I got on to O'Reilly, I was like a kid in a candy store. There are playlists. There are answers. There's on-demand training. It's worth its weight in gold, in terms of what it allows me to do.