July 2026
Intermediate
480 pages
20h 9m
English
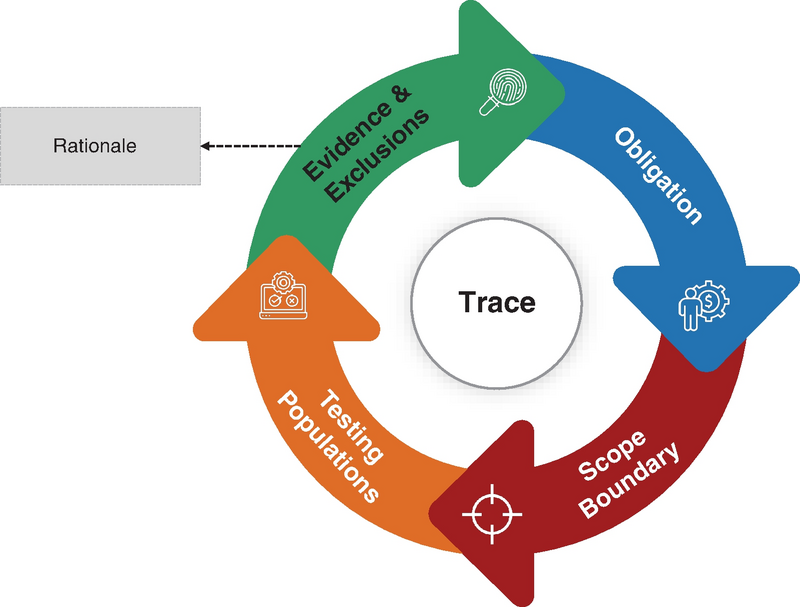
Sector overlays define how cybersecurity auditing adapts to the unique legal, operational, and evidentiary expectations of regulated industries. Financial services, healthcare, government, and payment systems each impose their own interpretations of risk and control assurance, transforming how auditors define scope, test effectiveness, and evaluate compliance. Understanding these overlays is essential to performing credible audits in environments governed by frameworks such as FFIEC, GLBA, HIPAA, HITRUST, FedRAMP, and PCI DSS. Each overlay translates general security principles into precise, enforceable obligations that dictate how systems are segmented, monitored, and authorized to operate.
Effective auditors learn to navigate these overlapping frameworks without losing sight of the common control foundation that underpins them. By recognizing where obligations converge and where they diverge, auditors can align evidence collection and testing approaches across multiple compliance programs. This discipline ensures that a single control—such as access management or encryption—can satisfy different regulatory expectations through sound documentation and traceable logic. The ability to reconcile conflicts, apply compensating controls, and maintain consistent conclusions across obligations reflects both technical skill and ...
Read now
Unlock full access


 O’Reilly covers everything we've got, with content to help us build a world-class technology community, upgrade the capabilities and competencies of our teams, and improve overall team performance as well as their engagement.I wanted to learn C and C++, but it didn't click for me until I picked up an O'Reilly book. When I went on the O’Reilly platform, I was astonished to find all the books there, plus live events and sandboxes so you could play around with the technology.I’ve been on the O’Reilly platform for more than eight years. I use a couple of learning platforms, but I'm on O'Reilly more than anybody else. When you're there, you start learning. I'm never disappointed.I'm always learning. So when I got on to O'Reilly, I was like a kid in a candy store. There are playlists. There are answers. There's on-demand training. It's worth its weight in gold, in terms of what it allows me to do.