July 2026
Intermediate
480 pages
20h 9m
English
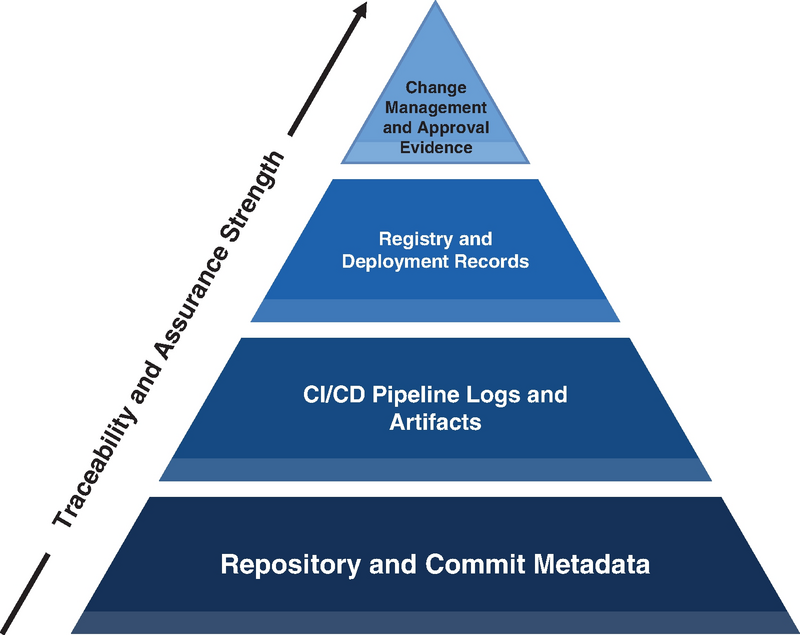
Software today is assembled and delivered at a speed and scale that outpaces traditional security oversight, making governance within the software development life cycle a central concern for auditors and risk professionals. Application and API ecosystems form the connective tissue of modern digital operations, and their security posture directly influences enterprise resilience. Understanding how development pipelines, code repositories, and runtime controls interlock is essential to validating whether an organization’s assurance claims are credible. This chapter examines the mechanisms that make software delivery verifiable, measurable, and enforceable from an audit perspective.
Modern cloud environments demand that policies, configurations, and reviews are embedded directly into the tools that create and deploy software. Automated controls—ranging from static and dynamic testing to dependency analysis and policy-as-code enforcement—replace informal approvals with machine-enforced evidence. By focusing on governed software pipelines, hardened environments, and structured release processes, this chapter illustrates how security becomes a built-in property of engineering rather than an afterthought. These practices allow auditors to trace accountability from the developer’s keyboard to the production endpoint, ensuring transparency across ...
Read now
Unlock full access


 O’Reilly covers everything we've got, with content to help us build a world-class technology community, upgrade the capabilities and competencies of our teams, and improve overall team performance as well as their engagement.I wanted to learn C and C++, but it didn't click for me until I picked up an O'Reilly book. When I went on the O’Reilly platform, I was astonished to find all the books there, plus live events and sandboxes so you could play around with the technology.I’ve been on the O’Reilly platform for more than eight years. I use a couple of learning platforms, but I'm on O'Reilly more than anybody else. When you're there, you start learning. I'm never disappointed.I'm always learning. So when I got on to O'Reilly, I was like a kid in a candy store. There are playlists. There are answers. There's on-demand training. It's worth its weight in gold, in terms of what it allows me to do.