July 2026
Intermediate
480 pages
20h 9m
English
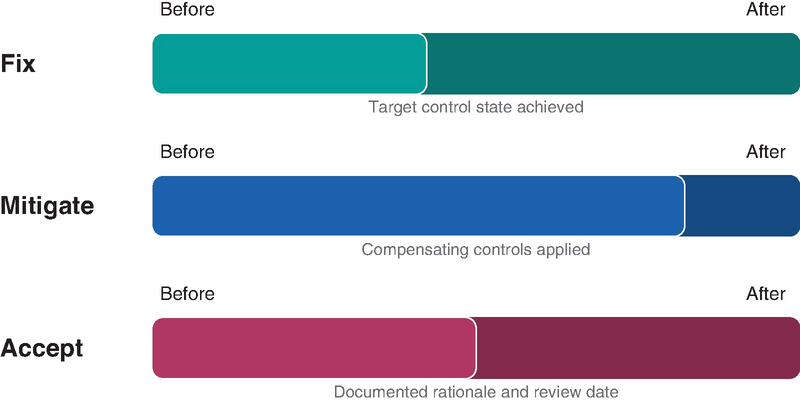
Effective audit reporting is where technical assurance becomes organizational decision-making. A finding that is meticulously gathered but poorly communicated loses its power to drive change, while a well-structured report can clarify priorities across business, compliance, and security leadership. This chapter examines how structured findings, severity calibration, and traceable evidence connect to residual risk and management accountability. Understanding these elements is essential to transforming audit work from documentation into actionable insight—linking assurance outcomes directly to enterprise risk management and governance oversight.
Modern cybersecurity programs operate at a scale and complexity that demand disciplined communication between auditors and executives. From the structure of individual findings to the framing of Board-level summaries, clarity and consistency determine whether audit results strengthen governance or simply add noise. This chapter emphasizes the mechanics of traceability, severity and materiality standards, recommendation quality, and management response design—ensuring that audit conclusions withstand scrutiny and inspire credible remediation. By standardizing these practices, organizations can ensure that every report tells a verifiable story about control effectiveness, business impact, ...
Read now
Unlock full access


 O’Reilly covers everything we've got, with content to help us build a world-class technology community, upgrade the capabilities and competencies of our teams, and improve overall team performance as well as their engagement.I wanted to learn C and C++, but it didn't click for me until I picked up an O'Reilly book. When I went on the O’Reilly platform, I was astonished to find all the books there, plus live events and sandboxes so you could play around with the technology.I’ve been on the O’Reilly platform for more than eight years. I use a couple of learning platforms, but I'm on O'Reilly more than anybody else. When you're there, you start learning. I'm never disappointed.I'm always learning. So when I got on to O'Reilly, I was like a kid in a candy store. There are playlists. There are answers. There's on-demand training. It's worth its weight in gold, in terms of what it allows me to do.