July 2026
Intermediate
480 pages
20h 9m
English
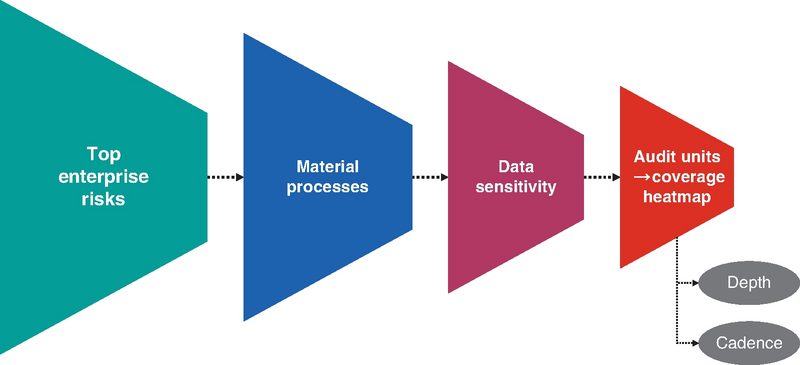
Annual audit planning is where the discipline of cybersecurity assurance transforms from isolated engagements into a coherent, risk-aligned strategy. Effective planning ensures that coverage, depth, and frequency of audits mirror the organization’s true risk landscape—not just its compliance obligations. By connecting enterprise risks, control maturity, and resource capabilities, the planning process converts abstract risk statements into actionable assurance activities. This alignment is critical for organizations that must demonstrate not only control effectiveness but also agility in responding to a rapidly shifting threat environment shaped by digital transformation and AI integration.
Sustained audit capability depends on more than scheduling—it relies on people, tools, and disciplined change management. From skill mapping and specialist sourcing to analytics enablement and evidence governance, a modern audit function must balance technical depth with operational efficiency. Automation, data-driven testing, and intelligent analytics expand coverage but also demand strong control over provenance, independence, and access. By integrating these elements into a unified planning framework, this chapter underscores how thoughtful design and resourcing transform the audit program from a compliance mechanism into a predictive, ...
Read now
Unlock full access


 O’Reilly covers everything we've got, with content to help us build a world-class technology community, upgrade the capabilities and competencies of our teams, and improve overall team performance as well as their engagement.I wanted to learn C and C++, but it didn't click for me until I picked up an O'Reilly book. When I went on the O’Reilly platform, I was astonished to find all the books there, plus live events and sandboxes so you could play around with the technology.I’ve been on the O’Reilly platform for more than eight years. I use a couple of learning platforms, but I'm on O'Reilly more than anybody else. When you're there, you start learning. I'm never disappointed.I'm always learning. So when I got on to O'Reilly, I was like a kid in a candy store. There are playlists. There are answers. There's on-demand training. It's worth its weight in gold, in terms of what it allows me to do.