July 2026
Intermediate
480 pages
20h 9m
English
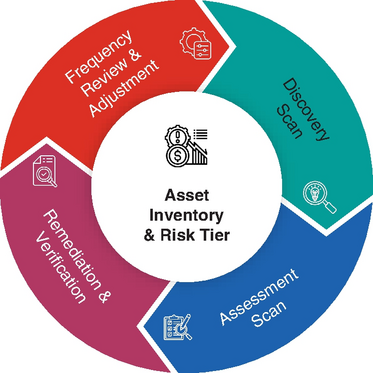
Vulnerability management and penetration testing oversight form the operational backbone of cybersecurity assurance. They transform abstract risk into measurable, testable evidence of control effectiveness. Understanding how assets are discovered, scanned, prioritized, and tested is essential to maintaining visibility in dynamic, hybrid environments where new systems appear as quickly as old ones are patched. The discipline described here turns technical scanning into governance—ensuring that every finding can be traced to an accountable owner, verified through remediation, and validated against defined service levels. This structured approach distinguishes organizations that merely identify weaknesses from those that can continuously prove they are being managed.
Modern enterprises cannot rely on severity scores alone to guide their response. Threat-informed prioritization models, such as those integrating Known Exploited Vulnerabilities (KEV) and exploit prediction data, allow teams to focus on what is actively being targeted, not just what looks dangerous on paper. Equally critical is the governance surrounding exceptions, risk acceptance, and testing independence. By establishing clear decision frameworks and evidentiary standards, organizations create an audit-ready posture—one where every deviation from policy has ...
Read now
Unlock full access


 O’Reilly covers everything we've got, with content to help us build a world-class technology community, upgrade the capabilities and competencies of our teams, and improve overall team performance as well as their engagement.I wanted to learn C and C++, but it didn't click for me until I picked up an O'Reilly book. When I went on the O’Reilly platform, I was astonished to find all the books there, plus live events and sandboxes so you could play around with the technology.I’ve been on the O’Reilly platform for more than eight years. I use a couple of learning platforms, but I'm on O'Reilly more than anybody else. When you're there, you start learning. I'm never disappointed.I'm always learning. So when I got on to O'Reilly, I was like a kid in a candy store. There are playlists. There are answers. There's on-demand training. It's worth its weight in gold, in terms of what it allows me to do.